
IdoubleS CTM · Cyber Threat Modelling platform
Governed Cyber Threat Model · Trust by Design
Security teams already have threat reports, feeds and AI. What is missing is governed knowledge, a customer-owned Cyber Threat Model that records what is known, why it is believed, how confident we are and whether it is validated enough to act on, bound to your critical business functions. IdoubleS turns CTI into that shared knowledge layer for humans and AI across detection, hunting, response and threat-led penetration testing. Trust by design, not by vendor assurance.
AI-native · Made in Germany · Runs where your data must stay
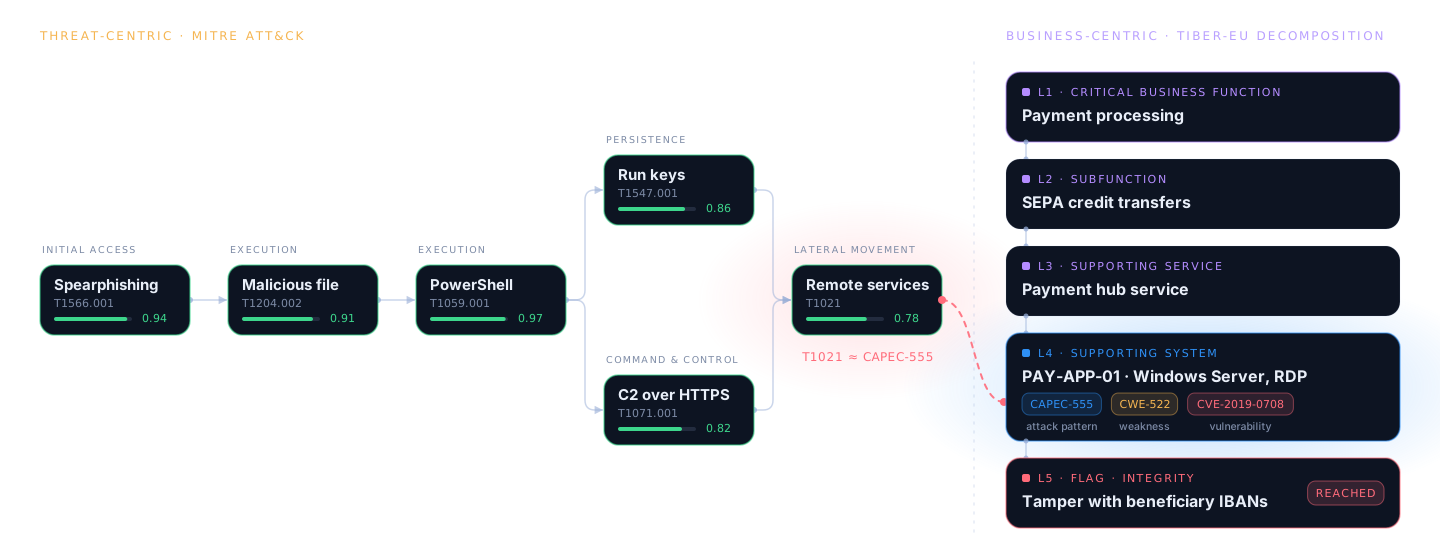
On the left you can find the adversary's techniques refined from a report. The right side of the table shows a critical business function decomposed the TIBER-EU way. The link is a claim, with its evidence, its confidence and an analyst's decision.
- CrowdStrike
- SVA System Vertrieb Alexander GmbH
- IBM Security
- Google Cloud
- Computacenter
- CrowdStrike
- SVA System Vertrieb Alexander GmbH
- IBM Security
- Google Cloud
- Computacenter
The 2026 DEBATE
Speed and volume are no longer the question. Trust is.
AI extracts a report in seconds and the result is acted on at machine speed. Yet the same report yields a different graph on the next run, four teams read it four ways, and nothing says where a claim came from or whether anyone checked it. Verified and plausible look alike. What a SOC needs is knowledge that is evidence-backed, traceable, validated and maintained, which no model supplies on its own.
- 01 · Representation
Many concepts, partial connections.
DML, ATT&CK, CAPEC, CWE, CVE and the Diamond Model each formalise one level or domain. Used in isolation or mapped inconsistently, they leave no coherent threat model, and reasoning across levels is unreliable for humans and AI alike. IdoubleS CTM is one governed representation on these standards, with meaning, relations, evidence and confidence per claim and links between the levels. Adopted as the model of record, it gives humans and AI consistent, reusable threat knowledge to reason on.
- 02 · AI-generated Knowledge
A model reads the report. Who vouches for what it wrote?
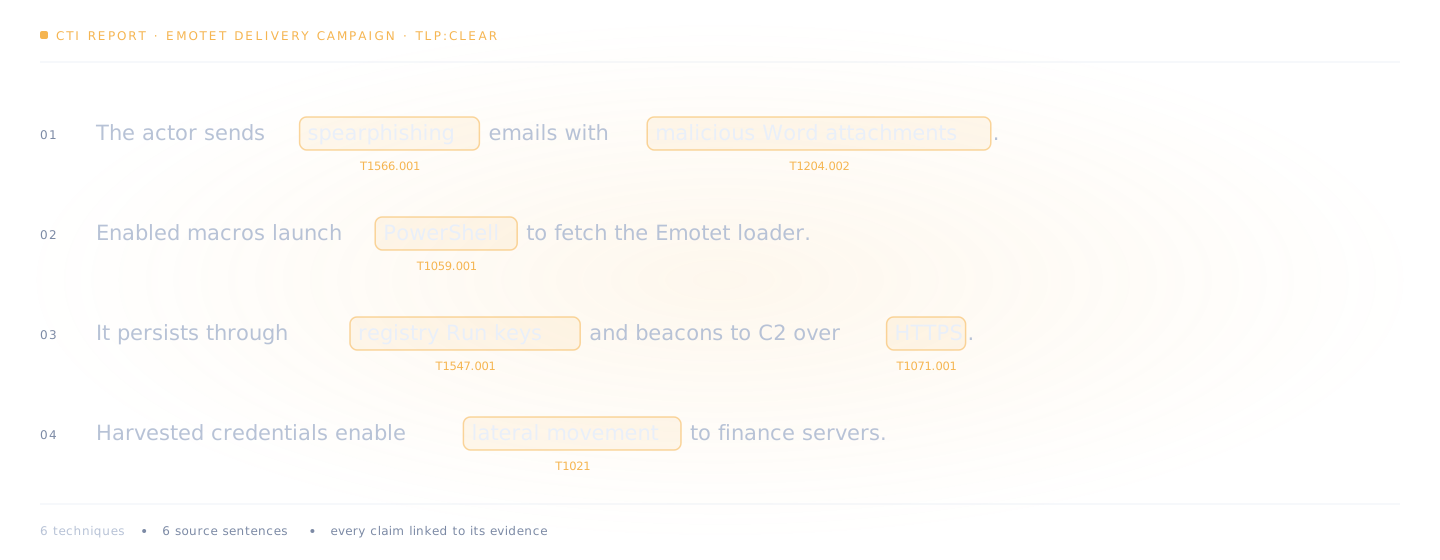
AI extraction is replacing the reading of threat reports, yet its output lacks reliability, confidence and validation. Unvalidated claims propagate at machine speed, and verified and plausible look alike. In IdoubleS CTM extraction writes into a schema. Every claim gets an identifier, its source, a confidence and a validation status, and an analyst validates it before it enters the model and the workflows. Trust by design, with fewer wrong detections and an auditable answer when the board asks how you know.
- 03 · Operational Reuse
Same intelligence, separate readings.
Triage, hunting, detection engineering, exposure management and response all turn intelligence into operational knowledge, each in its own tools and vocabulary. The same threat is prioritised and acted on differently, with duplicated effort, inconsistent coverage and gaps between teams. IdoubleS CTM transforms intelligence once into attack graphs bound to your critical business functions and reuses them everywhere as the single source of truth. One model, coordinated defence, with aligned priorities and faster, more consistent decisions.
- 04 · Ownership and Interoperability
Whose asset is your threat knowledge?
Organisations run a diverse security stack, and the knowledge behind each capability stays embedded in its vendor's ecosystem, hard to share and reuse. Dependency grows, and when a technology or provider changes the knowledge goes with it. IdoubleS CTM is a vendor-agnostic Cyber Threat Model, the shared knowledge layer between threat intelligence and security operations. Integrated over open standards and interfaces, it keeps governed threat knowledge reusable across CTI sources and security technologies. Change the platform, keep the knowledge.
- 05 · Deployment and Sovereignty
Data residency is not sovereignty.
Security platforms are increasingly cloud-delivered, while organisations work under different regulatory, operational and sensitivity requirements. Regional processing answers the residency question but not who controls data, models and knowledge, so organisations bend to the vendor's architecture or hold back sensitive data. IdoubleS CTM deploys to requirement, in the cloud, on-premises or air-gapped, on open standards and open-source frameworks, with data, AI models and the governed knowledge kept in your environment. You decide where your data and knowledge reside.
Proven, not assumed
Measured with the customer, against a jointly worked out baseline.
- 0%
exact baseline match of techniques. Emotet Delivery scenario, average of six automated runs. Ryuk Ransomware reached 84%.
- +0%
additional correct techniques found by the platform and confirmed by analysts, missed in four weeks of careful manual work.
- 11 of 11
native rules fired in adversary emulation. Every rule produced an offense in the customer's SIEM when the technique was executed. None stayed silent.
- 0%
quality of the native SIEM rules, rated over seven criteria by independent SIEM specialists, with little manual adjustment needed.
Results from our reference project in the German defence sector, 2025–2026. Read the reference project →
The platform
One governed model. Two sides. One bridge.
The threat-centric side models the adversaries relevant to you. The asset-centric side models what must be protected. Where the two meet, you see which current campaign can reach which critical business function, and every claim along the way keeps its evidence, its confidence, and an analyst's decision.
Threat-centric
Who would attack you, and how.
Relevant threat actors ranked from your business parameters, each with a rationale, and attack graphs refined from the reports you already receive.
The bridge
Which campaign can reach which function.
Exposure ranked by adversary relevance based on motivation and intent rather than by CVSS alone, with a scenario per actor and function.
Asset-centric
What must be protected.
Critical business functions decomposed the way DORA and TIBER-EU describe them, with the systems, components, and weaknesses that support them.
Who it is for
One model, coordinated defence.
CISO · Board
Defence posture you can evidence
One narrative per critical business function. Who threatens it, how, what we detect and what we test, with a lineage from intelligence to control for DORA, NIS2 and TIBER-EU.
See the use casesRisk manager
Exposure per critical business function
Weaknesses and paths ranked by adversary relevance based on motivation and intent. The same model the SOC and the red team use, so there is no parallel truth.
Exposure managementHead of CDC · SOC
Coverage, precision, capacity
Coverage counted per adversary and technique, validated rules with fewer noisy alerts, and hunting and response starting points from validated claims.
Detection engineeringTLPT · Red team
Threat-led penetration testing, repeatable
Threat profiles and scenarios per critical business function, traceable to the sources. The next test cycle starts from the model, not from a blank page.
Threat-led testing
Sovereign by construction
German startup, privately financed with German capital. Built on open-source frameworks.
Sovereignty has become the deciding criterion for German and European security leaders, and it is not a question of data location alone. It is about who controls the knowledge, the models, and the dependencies. IdoubleS is a German company, privately financed with German capital, building consistently on open-source frameworks and without dependence on proprietary code. Deploy to requirement, keep the model as your own asset in open standards.
About IdoubleSFinancing
Private German capital
No venture round, no foreign investor on the roadmap.
Foundations
Open-source frameworks
Auditable foundations instead of proprietary code.
What customers say about us
In their words.
“The flood of CTI reports used to be impossible to handle by hand. Today the IdoubleS platform refines it into a model we trust: traceable to the source, scored with confidence, validated by analysts, and at a quality and speed that were unthinkable before.”
Head of Cyber Defence Center, reference customer, German defence sector
Start where it counts
One critical business function. Its relevant adversaries. Two use cases.
A scoped pilot in the deployment mode your requirements dictate, measured against your own criteria, then scaled across detection, hunting, response, and threat-led testing.
Free webinar and workshop series
Intelligence-driven Cyber Threat Modelling at it-sa Expo&Congress 2026
Two online webinars and an onsite workshop in Nuremberg with IdoubleS, CrowdStrike, SVA, and a reference customer from the German defence sector. In German and English, free of charge, and with a complimentary copy of the accompanying book.
- 14 OctWebinar 1 · CTI and the Cyber Threat Model · online
- 21 OctWebinar 2 · Frameworks to a governed model · online
- 27 OctOnsite workshop · German · Nuremberg
- 28 OctOnsite workshop · English · Nuremberg
Contact
Operationalise Cyber Threat Intelligence.
Turn the reports and feeds you already receive into a governed Cyber Threat Model that your SOC and risk and management teams can act on. Tell us where you want to start.